The category mistake most buyers make .
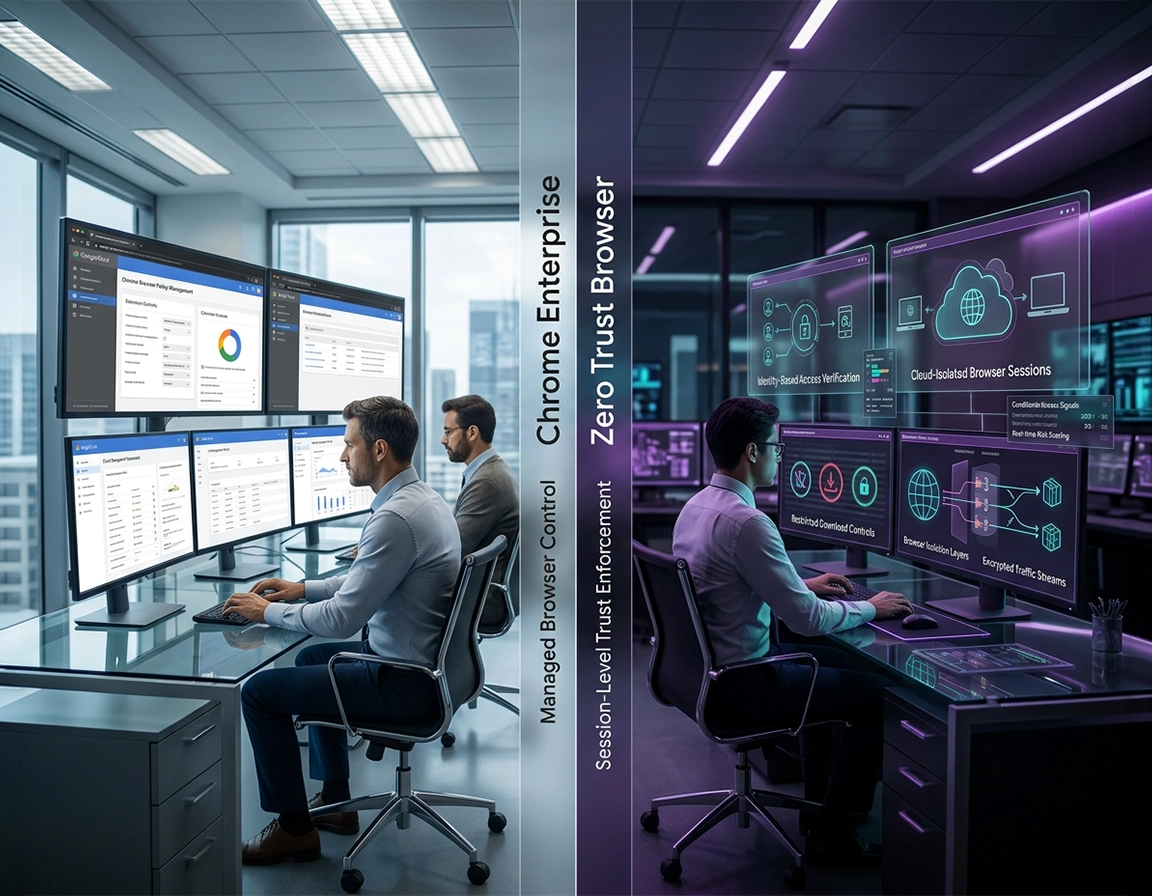
Chrome Enterprise and “zero trust browser” get compared as if they are direct substitutes. That is usually the first mistake in the evaluation. Chrome Enterprise is primarily a managed enterprise browser platform. It is about making Chrome deployable, governable, measurable, and supportable at scale. A zero trust browser is usually a trust model or security layer that pushes access policy, session restrictions, and data handling controls directly into the browsing experience.
Those two things can overlap, but they do not start from the same problem statement. Chrome Enterprise starts by asking how to run Chrome as a controlled enterprise asset. A zero trust browser starts by asking how to reduce implicit trust in the browser session itself. That distinction changes your requirements, your shortlist, your rollout owner, and often your budget line.
This is why enterprise teams end up talking past each other. Endpoint engineering may be focused on browser policy inheritance, extension allowlists, update control, profile management, and version consistency. Security architects may be focused on contractor access, unmanaged endpoints, SaaS session restrictions, clipboard controls, and browser isolation. Procurement hears the word “browser” in both meetings and assumes the same platform should solve both.
The more accurate framing is this: Chrome Enterprise manages the browser estate; zero trust browser controls manage trust conditions inside the browser session. Once you adopt that framing, the comparison becomes much cleaner.
Related: For the managed browser side of the discussion, start with Chrome Enterprise Guide, Chrome Enterprise Management, Chrome Enterprise Security Architecture, and Chrome Enterprise Features Explained.
Terms that need to be separated early .
- Managed browser: centrally administered browser with policy control, version management, extension governance, and operational reporting.
- Zero trust browser: browser or browser security layer enforcing identity-aware access, session restrictions, and least-privileged interaction with applications and data.
- Browser-layer DLP: restrictions on copy, paste, download, upload, print, or data transfer through the browser.
- Browser isolation: isolating risky or sensitive web activity away from the endpoint or constraining how rendered content can be interacted with.
- Device posture: endpoint trust signals such as management state, security tooling, OS health, or compliance status used to influence access.
Fast answer for security and procurement teams .
If your environment already runs Chrome widely and the main gap is inconsistent browser control, Chrome Enterprise is normally the better first decision. It addresses policy sprawl, browser drift, weak extension governance, inconsistent settings, and poor browser visibility without forcing a new browsing habit on employees.
If your main gap is that too many people access sensitive web apps from endpoints you do not fully trust, or if the browser session itself must enforce download, copy, paste, print, upload, and session path restrictions, then a zero trust browser model deserves higher priority. That is particularly true for contractors, external vendors, offshore teams, merger environments, partner access, and BYOD-heavy workflows.
Chrome Enterprise belongs at the center when you need
- Large-scale browser policy management
- Extension approval workflows, allowlists, and blocklists
- Standardized browser configuration across managed endpoints
- Better operational inventory of Chrome versions, profiles, and policy state
- A lower-friction path to improve browser security without replacing Chrome as the user standard
Zero trust browser controls belong at the center when you need
- Continuous re-evaluation of access based on identity and device posture
- Safer access from unmanaged or weakly trusted devices
- Browser-layer restrictions for downloads, clipboard use, upload paths, and printing
- More controlled access to sensitive SaaS, admin consoles, and internal web applications
- Isolation or session containment for risky browsing and third-party access
Related: Continue with Chrome Enterprise Zero Trust, Chrome Enterprise Access Control, Chrome Enterprise Session Management, and Chrome Zero Trust Browser Setup.
Browser governance versus trust enforcement .
Chrome Enterprise is strongest when the browser itself needs discipline. That means deployment control, policy centralization, profile consistency, extension governance, update management, version rollback planning, and browser telemetry that actually helps IT understand what is running in the field. In environments with rapid app adoption and weak change control, that alone can materially reduce risk.
A zero trust browser design is strongest when the session must behave differently based on who the user is, where they are coming from, which device they are using, what application they are accessing, and what actions they should be allowed to take once the page loads. In that model, the browser is not just a client. It becomes part of the trust enforcement surface.
Chrome Enterprise emphasizes
- Browser fleet consistency
- Policy enforcement
- Extension governance
- Version and rollout control
- Operational visibility for IT
Zero trust browser emphasizes
- Identity-aware access decisions
- Device trust and posture checks
- Session-level restrictions
- Browser-layer DLP
- Constrained or isolated access to sensitive apps
The reason this matters is practical, not academic. If your board-level concern is shadow extension risk, unmanaged browser settings, and support chaos, a zero trust browser pilot will often feel like the wrong tool, even if it is technically sophisticated. If your board-level concern is contractor exposure to finance systems or customer data leaving SaaS sessions through copy and download actions, managed browser hygiene alone will not satisfy the requirement.
Related comparisons: Chrome Enterprise vs Secure Browser, Chrome Enterprise vs SASE Solution, Chrome Enterprise vs Virtual Browser, and Chrome Enterprise Managed Browser Solutions Overview.
Enterprise comparison matrix .
The cleanest shortlist comes from comparing the control domains that actually influence architecture, compliance scope, and rollout ownership. This is where vague positioning language stops being useful.
| Control domain | Chrome Enterprise | Zero trust browser | Why it matters |
|---|---|---|---|
| Browser policy governance | Excellent | Usually secondary | If the core requirement is consistent browser settings, profile control, and policy inheritance across a large estate, Chrome Enterprise is typically the stronger fit. |
| Extension governance | Excellent | Often less central | Allowlisting, forced installs, host permission review, and extension sprawl control are major reasons enterprises adopt managed browser tooling. |
| Browser inventory and telemetry | Strong | More focused on access and risk events | Security teams need access analytics; IT teams need browser fleet visibility. Those are not always the same thing. |
| Identity-aware access | Possible through surrounding enterprise security stack | Usually core to the model | If identity and device posture must shape every session, zero trust browser logic is generally more native. |
| Unmanaged endpoint tolerance | Moderate, depending on design | Usually stronger | BYOD, partner access, and contractor workflows push the evaluation toward session restriction and trust minimization. |
| Browser-layer DLP | Can be strong when paired with advanced protections | Frequently a headline capability | Testing should focus on real actions: clipboard, download, upload, print, screen capture, and session persistence. |
| Browser isolation | Not usually the platform’s defining identity | Often a differentiator | If isolation is mandatory for risky sites or sensitive sessions, this control should be validated directly in pilot. |
| User familiarity | Excellent | Varies by implementation | User friction matters because enterprise security value disappears quickly when adoption collapses or workarounds spread. |
| Operational ownership simplicity | Simpler for IT-led programs | More cross-functional | Zero trust browser rollouts often need IAM, app owners, security engineering, and workplace teams aligned from day one. |
What this matrix usually exposes .
If most of your scored requirements sit in policy management, extension governance, browser inventory, and deployment control, then your program is browser-administration-heavy and Chrome Enterprise should usually anchor it. If most of the scored requirements sit in conditional access, unmanaged device control, sensitive session restrictions, and app-level trust decisions, then your program is really a zero trust access and browser security initiative.
That distinction matters because it changes the questions your pilot should answer. Managed browser pilots should measure policy coverage, extension cleanup, update consistency, support burden, and browser standardization. Zero trust browser pilots should measure SaaS usability under restriction, contractor access safety, DLP enforcement, device-trust branching, and app compatibility under constrained sessions.
Where Chrome Enterprise fits best .
Chrome Enterprise is often the right answer when the organization’s real weakness is not sophisticated attacker tradecraft, but weak browser governance. That sounds less dramatic, but in large estates it is frequently the higher-probability risk.
Browser standardization across distributed fleets .
If teams are effectively running different browser baselines, the company loses policy consistency, support predictability, and security confidence. Chrome Enterprise is well suited to environments where browser settings, update timing, extensions, profile behavior, certificate handling, and Safe Browsing-related posture need to be made consistent across business units.
Extension risk and permission sprawl .
Many browser incidents are extension incidents in disguise. Employees accumulate AI helpers, research tools, coupon add-ons, password assistants, tab managers, and workflow plug-ins that request broad host permissions or gain access to page content across sensitive domains. If that is the immediate attack surface, Chrome Enterprise is often more relevant than a platform optimized around session restriction but not extension governance.
Managed endpoint environments .
Where employees already use company-managed laptops with mature endpoint controls, the urgent browser question often becomes governance rather than trust minimization. In those environments, Chrome Enterprise usually produces the cleaner administrative outcome and lower user friction.
Browser maturity before zero trust layering .
Security teams sometimes try to jump into zero trust browser language before the browser estate itself is visible and controllable. That can produce an expensive overlay on top of weak browser operations. If you do not yet have reliable browser policy coverage, extension governance, or version discipline, Chrome Enterprise often belongs earlier in the maturity path.
Where zero trust browser controls win .
Zero trust browser controls are at their strongest when trust cannot be assumed at login and cannot be assumed from the endpoint. These are the environments where sensitive applications, external users, and mixed-trust devices are normal operating conditions rather than fringe exceptions.
Contractor, vendor, and partner access .
External users frequently access internal or SaaS systems from unmanaged devices. In that scenario, browser governance alone is not enough. The session itself needs rules: read-only access, blocked downloads, restricted clipboard usage, controlled uploads, maybe even isolated rendering or app segmentation. This is classic zero trust browser territory.
Sensitive data inside browser sessions .
Finance dashboards, support consoles, customer records, code repositories, HR systems, and privileged admin tools all create the same question: what can the user actually do with the data once the page is open? If your answer depends on identity, role, device state, or risk context, then the session needs to become a policy surface, not just the browser configuration.
Mixed-trust device environments .
Mergers, temporary staffing, offshore operations, field teams, and urgent access requests produce environments where not every endpoint deserves the same trust. Zero trust browser controls become more relevant when the browser session must compensate for that uneven device posture.
High-control web access models .
If the organization wants policy branching such as full access on managed devices, restricted access on personal devices, and isolated access for risky sessions, then the evaluation is no longer just about browser management. It is about building a browser-mediated access model.
Isolation as a mandatory control .
When security requirements explicitly mention browser isolation for unknown sites, third-party research, or sensitive app workflows, a zero trust browser or adjacent secure browsing architecture usually becomes central to the shortlist. That control should not be inferred from marketing language; it should be tested directly in production-like scenarios.
Related: Continue with Chrome Enterprise Secure Remote Access, Chrome Enterprise for Contractors, Chrome Enterprise Browser Isolation Guide, Chrome Enterprise Remote Workforce, and Best Managed Browser for Enterprise.
Operating model, ownership, and rollout sequence .
One reason these projects go sideways is that they look similar in a slide deck but land in different operating models. Chrome Enterprise generally fits an endpoint or workplace engineering motion. Zero trust browser rollouts are usually more cross-functional, with deeper IAM and security architecture involvement.
Chrome Enterprise rollout sequence .
- Standardize supported browser deployment paths.
- Centralize browser policies and profile behavior.
- Rationalize extensions, permissions, and forced-install requirements.
- Align update cadence, rollback planning, and browser support processes.
- Add deeper security controls once browser governance is stable.
This path is operationally attractive because the ownership model is familiar. It feels like a browser administration program with measurable security outcomes.
Zero trust browser rollout sequence .
- Classify applications and user groups by sensitivity and business risk.
- Define device posture and identity signals that should influence access.
- Map session restrictions for view, copy, download, print, upload, and navigation behavior.
- Pilot contractors, vendors, and unmanaged endpoint scenarios first.
- Validate app compatibility, user friction, and exception handling before expanding.
This path is harder to fake and harder to rush. It requires agreement between security, IAM, workplace IT, app owners, and sometimes legal or compliance functions. That does not make it worse. It just makes it different from a browser policy project.
Why combined deployments are common .
Many mature organizations land on a split model. Managed Chrome becomes the standard for employees on corporate endpoints. Zero trust browser controls are applied when access is weaker-trust, more sensitive, or more externally exposed. That keeps the employee browsing experience familiar while still tightening riskier access paths.
Questions your architecture team should answer before purchase .
- Are we solving a browser-administration problem or a sensitive-session problem?
- How much of our critical access happens on endpoints we do not fully trust?
- Is extension governance one of our highest-probability browser risks?
- Do we need policy branching by user, app, and device posture?
- Is browser isolation optional, selective, or mandatory?
- Who owns exceptions and user friction once the platform is live?
Risk, data handling, and compliance implications .
This comparison is not only about security. It also changes how your organization treats session visibility, data movement, contractor trust, and compliance evidence. The stricter your browser control model becomes, the more important it is to decide what is being enforced, what is being monitored, and how that is governed internally.
Impact: Affects browser governance, contractor exposure, session DLP, extension risk, remote access design, and audit posture around web applications.
Chrome Enterprise risk reduction .
Chrome Enterprise reduces risk by making the browser less chaotic. Stronger policy coverage, governed extensions, controlled updates, standard profile behavior, and better visibility into browser state reduce the chance that browsers become unmanaged exceptions inside an otherwise controlled environment. For many enterprises, that is not a minor win. It is the missing layer between endpoint policy and user behavior.
Zero trust browser risk reduction .
A zero trust browser model reduces risk by moving access scrutiny closer to the work itself. Rather than assuming the user session remains safe after login, it continues to shape what the session can do. That matters most when the browser is the primary doorway into sensitive SaaS, internal web apps, or privileged interfaces.
Compliance and audit relevance .
Compliance teams rarely care about browsers as a category. They care about repeatable controls. Chrome Enterprise helps when audit questions revolve around browser policy consistency, extension governance, and centrally enforced configuration. Zero trust browser controls help when audit questions revolve around controlled access to regulated applications, restricted data movement, and differentiated treatment of trusted versus untrusted endpoints.
Privacy and workforce communication .
The more a browser session becomes a security control point, the more important governance becomes around logging, restrictions, monitoring visibility, and employee communication. That is not an argument against zero trust browser controls. It is an argument for clarity. Security teams should be explicit about what is enforced, what is inspected, and where exceptions exist.
| Environment type | Preferred anchor | Main reason | Typical second phase |
|---|---|---|---|
| Managed employee fleet | Chrome Enterprise | Highest return usually comes from browser standardization, extension governance, and operational visibility | Selective trust-based controls for sensitive apps |
| Contractor-heavy environment | Zero trust browser controls | Session restrictions matter more because endpoint trust is weaker | Managed Chrome where possible for internal staff |
| Regulated SaaS-heavy workflow | Combined model | Needs both policy consistency and data movement control inside the browser | Broader app classification and exception handling |
| Fast-growth enterprise with messy browser operations | Chrome Enterprise first | Operational cleanup typically delivers the quickest measurable uplift | Deeper session restrictions for high-risk cohorts |
Related: Chrome Enterprise Compliance, Chrome Enterprise GDPR Compliance, Chrome Enterprise HIPAA Compliance, Chrome Enterprise SOC2 Compliance, Chrome Enterprise Data Loss Prevention, Chrome Enterprise Data Governance, and Chrome Enterprise Audit Preparation.
Avoidable buying mistakes .
Confusing product language with control coverage .
“Secure browser,” “enterprise browser,” and “zero trust browser” are not precise procurement terms. Build your evaluation sheet around control coverage, not category labels.
Ignoring extension governance because it sounds less strategic .
In many enterprises, uncontrolled extensions are a bigger immediate risk than unknown-site browsing. If extension permissions, host access, and install workflows are messy, Chrome Enterprise may eliminate more practical risk than a more dramatic architecture shift.
Piloting only on clean, managed endpoints .
This hides the exact workflows that justify zero trust browser investment. Every serious pilot should include unmanaged devices, contractors, external users, and one or two sensitive SaaS applications where data handling restrictions actually matter.
Leaving app owners out of the process .
Session restrictions that look ideal in security review can break export workflows, help desk operations, vendor support tasks, or finance reporting habits. Browser control cannot be evaluated in isolation from application behavior.
Assuming one platform replaces the other by default .
Many organizations do not need a single winner. They need the right control layer in the right place. Managed Chrome for employee standardization and zero trust browser controls for higher-risk access is often the most rational outcome.
FAQ .
Is Chrome Enterprise itself a zero trust browser?
Not in the strict category sense. Chrome Enterprise is first and foremost a managed enterprise browser platform. It can support zero trust architecture, but the broader zero trust browser category usually emphasizes conditional access, session restrictions, and device-trust-aware controls more explicitly.
Can Chrome Enterprise be part of a zero trust design?
Yes. That is often the most practical enterprise outcome. Chrome becomes the governed browser layer, while identity, device posture, session control, and data handling restrictions form the zero trust layer around higher-risk access paths.
Which option is stronger for contractors and partner access?
Zero trust browser controls usually have the edge here because the session can be restricted even when the endpoint is unmanaged or only partially trusted. That is much harder to solve with browser governance alone.
Which option is stronger for extension control and browser standardization?
Chrome Enterprise is usually stronger for that specific requirement set. If the primary need is policy consistency, extension governance, update control, and visibility into browser posture, managed Chrome generally fits better.
Do most mature organizations end up with one platform or a combination?
Many end up with a combination. They standardize Chrome for employees and managed endpoints, then use stricter trust-aware controls for sensitive apps, external users, contractors, or sessions where data movement must be tightly restricted.
Sources & further reading .
- Chrome Enterprise official overview
- Chrome Enterprise admin help and policy documentation
- Chromium browser administration resources
- NIST cybersecurity and zero trust guidance
- CISA enterprise security guidance
Editorial note: This page is written for enterprise evaluation and architecture planning. Packaging, control names, and deployment models change over time, so high-intent buyers should validate shortlisted controls through live pilot scenarios rather than through category labels alone.