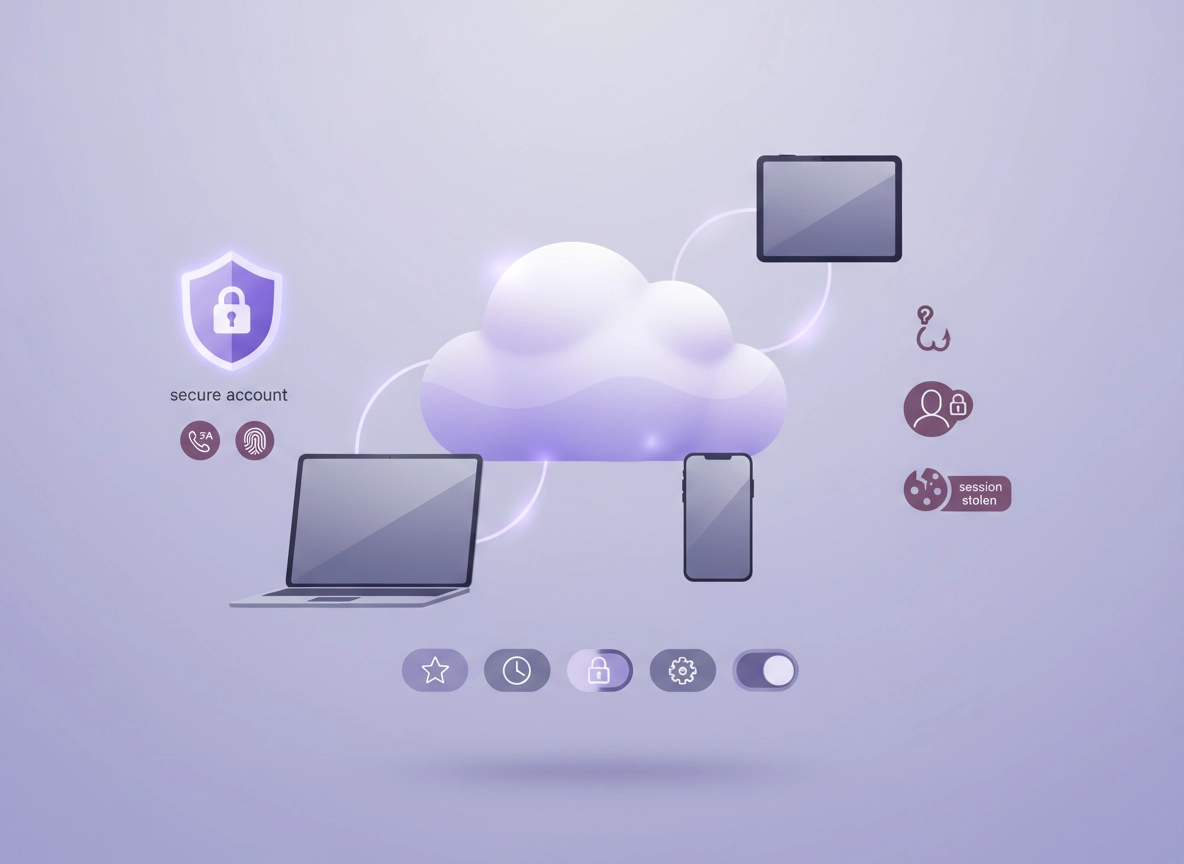
What Chrome Sync is (and why the risk is misunderstood) .
Chrome Sync is not “just a browser feature.” It’s an account feature.
Chrome Sync is the system that keeps your Chrome profile consistent across devices. When it’s enabled, Chrome can copy selected data types (like bookmarks, extensions, saved passwords, address bar suggestions, and certain settings) to your Google account, and then download them onto other devices where you sign in.
That’s the convenience. The risk comes from a simple reality: once Sync is enabled, your browser data becomes portable. If someone gains access to your Google account (or to a device that stays signed in), they don’t need to “hack Chrome.” They can simply sign in and let Sync deliver what they want—sometimes quietly, sometimes instantly.
Most discussions about Chrome Sync security focus on encryption in transit (which is standard) and forget the bigger picture: account compromise, device trust, and what you chose to sync. If you sync sensitive categories (passwords, payment methods, autofill, browsing history) but treat your Google account like a casual login, your attack surface is much larger than you think.
Related: Sync is closely tied to your sign-in protections. If you haven’t reviewed them recently, start here: Chrome sign-in security settings and Chrome two-factor authentication guide.
Key terms (quick definitions) .
- Chrome profile: The local container for your browser identity (bookmarks, extensions, settings, cookies, and more).
- Sync (Chrome Sync): The service that uploads selected profile data to your Google account and downloads it to other signed-in devices.
- Sync types: The categories you can enable/disable (e.g., bookmarks, passwords, history, extensions, settings).
- Account takeover (ATO): When an attacker gains access to your Google account (phishing, stolen cookies, reused passwords, SIM swap, etc.).
- Session theft: When an attacker steals an authenticated browser session token—so they can access your account without your password.
- End-to-end encryption (E2EE): Encryption where only your devices can decrypt the data (not the service provider). Some Sync data can be protected with an encryption passphrase depending on your setup.
Top risk scenarios (how Sync actually gets abused) .
If you want practical security, focus on realistic attacker paths. Below are the most common ways Chrome Sync becomes a problem, plus the best defense for each.
1) Phishing your Google account .
This is the classic: a fake sign-in page, a malicious OAuth consent screen, or a “your account is locked” email. If the attacker gets your Google credentials (or tricks you into approving a login), they can sign into Chrome on their own device and Sync your data.
- Why Sync makes it worse: It turns a single stolen login into a multi-device data pull.
- Best defense: Passkeys or hardware keys + 2-step verification + security alerts, plus removing unknown devices regularly.
2) A shared PC or “just for a minute” device .
Hotels, classrooms, a friend’s laptop, a coworker’s machine—Sync is dangerous when you sign in anywhere you don’t fully control. Even if you sign out, traces can remain (downloads, cached data, cookies, or an accidentally left-on profile).
- Why Sync makes it worse: You can unintentionally deposit sensitive data onto an untrusted endpoint.
- Best defense: Use Guest Mode, a separate “travel” profile, or don’t enable Sync on untrusted endpoints. Consider private browsing alternatives for safer workflows.
3) Lost/stolen device that stayed signed in .
If your laptop is stolen while unlocked (or your phone is stolen while Chrome remains authenticated), the attacker doesn’t need your password. They already have a live session. This is where “device trust” matters.
- Why Sync makes it worse: A stolen device can receive future Sync updates and also expose current local data.
- Best defense: Strong device lock, disk encryption, OS-level security, and immediate account action: remove device access and sign out remotely where possible.
4) Malware / info-stealers targeting browsers .
Modern malware often targets browsers because browsers hold sessions and credentials. Some steal cookies (sessions), others target saved passwords. If malware lands on a device where Chrome is signed in with Sync enabled, the attacker can extract value fast.
- Why Sync makes it worse: Sync increases the amount of high-value data present (or soon-to-be present) on the compromised endpoint.
- Best defense: Reduce synced categories on risky endpoints, use a hardened profile, and follow a cleanup playbook if you suspect compromise.
Related: If you think the device might be compromised, don’t “tweak settings” first—contain and clean: Chrome infected with malware: what to do and Remove malware from Chrome.
5) Enterprise risk: personal Sync on corporate data .
In business environments, the risk is often policy-based: an employee signs into Chrome with a personal Google account on a work machine, enabling Sync. Now corporate bookmarks, SaaS admin URLs, and potentially credentials end up tied to personal identity and devices.
- Why Sync makes it worse: It creates uncontrolled data replication outside IT governance.
- Best defense: Managed profiles, Chrome Enterprise policies, and blocking or restricting Sync where required.
Related: If you manage devices, read Chrome Enterprise security settings and managed browser security.
Before you start (fast checks) .
These checks take 2–5 minutes and prevent wasted time. They also tell you whether you should harden Sync, reset it, or disable it.
- Check 1: Are you signed into Chrome with a personal Google account, a work account, or both? (Multiple profiles often create confusion.)
- Check 2: Are there any devices you don’t recognize signed into your Google account? If yes, treat it as a potential compromise.
- Check 3: Are you syncing passwords/autofill/payment methods? If yes, your “minimum security bar” is higher.
- Check 4: Is this a shared or unmanaged device (school PC, borrowed laptop, contractor BYOD)? If yes, avoid enabling Sync.
- Check 5: Do you rely on Sync for productivity? If yes, use a safer configuration instead of turning everything off.
Related: If you want the baseline safe setup first, start with Chrome account sync settings and default security settings guide.
Step-by-step: harden Sync the safe way .
This is the recommended path for most people: keep Sync for convenience, but reduce what it carries and harden the account boundary. If you suspect compromise, follow the “incident” steps too (they’re marked).
- 1 Open Sync settings in Chrome.
Desktop: ⋮ → Settings → You and Google → Sync and Google services (or Sync / Manage what you sync).
Mobile: ⋮ → Settings → Sync (paths vary slightly). - 2 Switch from “Sync everything” to selective Sync.
Turn off categories you don’t need. If you’re unsure, start by disabling: History, Open tabs, Payment methods, and (for many users) Passwords. - 3 Secure your Google account before you trust Sync.
Enable 2-step verification (or passkeys), review security alerts, and remove unknown devices. If you use Sync for passwords, raise your security bar: passkeys/hardware keys are worth it. - 4 Review password security (if password sync is enabled).
Run password checks, remove weak/reused passwords, and clean up old logins you no longer use. A synced password vault is only as safe as your account boundary. - 5 Audit extensions (because Sync can reinstall them).
Remove unused extensions and review permissions for the ones you keep—especially “Read and change all your data on all websites.” - 6 Use separate Chrome profiles for separate risk zones.
Example: a Work profile (managed, strict), a Personal profile (normal), and a Travel profile (minimal, no password sync). This prevents accidental cross-contamination. - 7 (If you suspect compromise) Reset Sync data and sign out everywhere.
If you see unknown devices, unexpected bookmarks, strange extensions, or “Sync error” prompts you didn’t trigger, treat it seriously: remove devices, change your Google password, and reset Sync to invalidate old encrypted data states where applicable.
What “success” looks like: Sync remains on, but only the categories you intentionally chose are syncing. Your account has strong sign-in protection, unknown devices are removed, and your Chrome profile is separated by purpose. If an attacker signs into Chrome, they don’t automatically receive your entire browsing life.
Related: If you want a safer baseline configuration, follow secure profile setup and profile security settings.
Common variations (Windows, macOS, mobile) .
- Windows / ChromeOS: You’ll usually see “You and Google” at the top of Settings. Some devices show a dedicated “Sync” row.
- macOS: The layout is similar; “Keychain” and OS-level password storage can affect how users think about password sync.
- Android / iPhone: Sync options are often grouped under your account name in Chrome Settings. Mobile also adds extra risk if your device lock is weak.
Advanced settings (power users & enterprise) .
This section is for users who want deeper control: encryption posture, hardened profiles, and enterprise guardrails. If you’re the person people call when “something weird is syncing,” this is where you earn your time back.
Related: For managed environments, see Chrome Enterprise guide and Chrome security policy setup.
1) Decide your Sync encryption posture .
Sync is typically encrypted in transit and at rest. Where teams get confused is who can decrypt the synced data. Depending on your setup and the data type, Sync may be protected using your Google account credentials, and some configurations allow a separate encryption passphrase for synced data. The security tradeoff is simple:
- More convenience: easier recovery, better integration (password manager access, cross-device features).
- More privacy: stronger encryption boundaries, but more lockout risk if you forget a passphrase.
Related: If you’re optimizing encryption end-to-end, also review Chrome data encryption settings.
2) Separate profiles for isolation (high impact, low effort) .
Many Sync incidents are self-inflicted: someone signs in “just once” on the wrong device, then Sync replicates their environment everywhere. Separate profiles prevent this. Here’s a proven structure:
- Work profile: strict extensions, minimal syncing, no personal browsing, protected by strong account controls.
- Personal profile: normal usage, but still selective sync (especially history/passwords depending on your risk tolerance).
- Travel / public profile: minimal bookmarks, no password sync, no payment info, no saved autofill.
3) Harden the account boundary (identity protection) .
Chrome Sync security is basically Google account security. That’s why identity hardening is the highest ROI move you can make. If you do one thing today, do this:
- Enable strong sign-in protection (2FA/passkeys; ideally hardware keys for high-risk users).
- Review security events and remove unknown devices immediately.
- Use unique passwords (no reuse) and clean up old accounts.
- Keep recovery options secure (recovery email/phone; avoid weak recovery paths).
Related: Follow the identity-focused path: identity protection guide and account security settings.
4) Enterprise controls (the “don’t let this happen” layer) .
In organizations, you typically want one of these outcomes: allow Sync but restrict it, allow Sync only on managed accounts/devices, or block Sync entirely. The right choice depends on compliance requirements and your endpoint trust model.
- Allow but restrict: Permit bookmarks/settings sync, block password/payment sync.
- Managed-only: Only allow Sync for corporate accounts on managed devices; block personal accounts from signing in.
- Block: In high-compliance environments, disable Sync and use managed alternatives for bookmarks/config distribution.
Related: If you’re building a policy baseline, read IT admin security settings and enterprise privacy controls.
Common alternatives users compare .
- Chrome password sync vs dedicated password managers
- Syncing everything vs a hardened “selective sync” profile
- Personal Google accounts vs managed enterprise accounts
- Browser Sync vs secure browser / managed browser platforms
Related: If you’re evaluating credential storage options, see password manager vs Chrome passwords and Chrome password manager security risks.
Privacy & security notes (tradeoffs) .
The goal isn’t to fear Sync—it’s to use it intentionally. A secure configuration is one where Sync doesn’t become a silent data pipeline. Below is the practical tradeoff map.
Impact: Affects credentials, browsing footprint, extensions, and cross-device identity.
Plain-English summary: If your Google account is protected (2FA/passkeys) and you only sync what you need, Chrome Sync is usually fine. The risk spikes when you sync sensitive categories to devices you don’t fully trust—or when an attacker can log into your account and let Sync do the work.
Recommended baseline settings .
- Option A (balanced): Sync bookmarks + settings + extensions (curated), keep history off, keep passwords on only if your Google account has strong 2FA/passkeys.
- Option B (maximum privacy): Sync bookmarks only (or disable Sync entirely), use a dedicated password manager, and keep separate profiles for work/personal.
- Option C (compatibility): Sync everything on trusted devices only, but lock down the account boundary and remove Sync from shared/unmanaged devices.
Recommended settings by goal .
| Goal | Recommended setting | Tradeoff | Best for |
|---|---|---|---|
| Balanced | Selective Sync: bookmarks + settings + curated extensions | Some features (history/tab sync) won’t follow you | Most users |
| Maximum privacy | Disable sensitive sync types (passwords/autofill/history) or disable Sync | Less convenience, more manual setup | High-risk users, journalists, executives, security-conscious teams |
| Compatibility | Keep Sync but restrict it to trusted devices only + strong sign-in protection | Still risky if a trusted device is compromised | Enterprise apps, finance/banking workflows |
Related: For a broader privacy posture, read Chrome privacy settings and Chrome privacy risks.
Troubleshooting .
Related: If your Sync issues are tied to sign-in or account prompts, review sign-in security settings.
If you see bookmarks you didn’t add .
This can come from a second profile/account, a previously used device still signed in, or an actual compromise. First, confirm you’re in the right Chrome profile (top-right avatar). Then check your Google account device list and remove anything unknown. If you still see unexpected data, consider resetting Sync and changing your Google password immediately.
If Chrome asks for a passphrase you don’t remember .
This typically happens if a custom encryption passphrase was set in the past. If you don’t have it, you may need to reset Sync data to regain access. This is why passphrase-based encryption increases privacy but also increases lockout risk. Before you reset anything, confirm you’re signed into the correct Google account.
If Sync keeps turning off or shows “Sync error” .
Common causes include account verification requirements, outdated Chrome versions, blocked cookies for Google services, or conflicts between profiles. Update Chrome, ensure Google sign-in isn’t blocked by privacy settings, and re-check “Sync and Google services.” If the error persists, remove and re-add the account to Chrome, then re-enable selective sync (not “sync everything”).
If you need to disable Sync safely (without losing local data) .
Disabling Sync can be safe, but make sure you understand what stays local and what won’t. On desktop, look for a “Turn off” option in Chrome settings. In many cases Chrome will ask if you want to remove synced data from the device. If you’re turning off Sync because the device is untrusted, you usually do want to remove the synced data from that device.
Related: Step-by-step disable instructions: Disable Chrome Sync.
If you suspect a real compromise .
Don’t overthink it. Assume the attacker can act faster than you. Prioritize containment: (1) change your Google password, (2) enable 2FA/passkeys if not already enabled, (3) remove unknown devices, (4) review saved passwords and revoke sessions where possible, and (5) reset Sync data if you cannot trust the current state. Then clean the endpoint (malware scan) before signing in again.
Related: Use a structured response: Chrome security audit guide and Chrome data breach protection.
FAQ .
-
helpIs Chrome Sync safe to use?It can be safe when your Google account is strongly protected and you only sync what you need. The biggest risks are account compromise, shared/untrusted devices, and syncing high-value categories like passwords, autofill, and payment methods without strong sign-in protection.
-
helpDoes Chrome Sync share my full browsing history?Sync can include history-related data depending on your settings. If you don’t want your browsing footprint replicated across devices, turn off the History (and tab-related) sync categories. Always verify what’s enabled under “Manage what you sync.”
-
helpWhat’s the biggest security risk with Chrome Sync?Account compromise. If an attacker gains access to your Google account (phishing, stolen session cookies, weak recovery), they can sign into Chrome and let Sync pull data onto their device. Strong 2FA/passkeys and device audits are the best defense.
-
helpShould I disable Chrome Sync completely?If you use shared/unmanaged devices, work in high-risk environments, or don’t need cross-device convenience, disabling Sync can be a smart move. Otherwise, a safer middle ground is selective Sync + strong account protection + separate Chrome profiles for work/personal/travel.
Sources & further reading .
- Google Chrome Help: Get your bookmarks, passwords, and more on all your devices (Sync overview)
- Malwarebytes: Browser sync—what are the risks of turning it on?
- Independent analysis: Chrome Sync privacy discussion (context and tradeoffs)
- Chromium issue tracker: Security concerns related to synced data behavior (technical context)
- Chrome privacy policy archive: Signed-in, synced Chrome mode (historical reference)
Disclosure: Some pages may mention tools or services. Recommendations are editorial and based on practical testing and security tradeoffs.